SIEM Comparison 2026: Splunk vs. Microsoft Sentinel vs. IBM QRadar
Every SOC runs on a SIEM — the platform that ingests logs from across an organization’s systems and turns them into alerts an analyst can actually act on
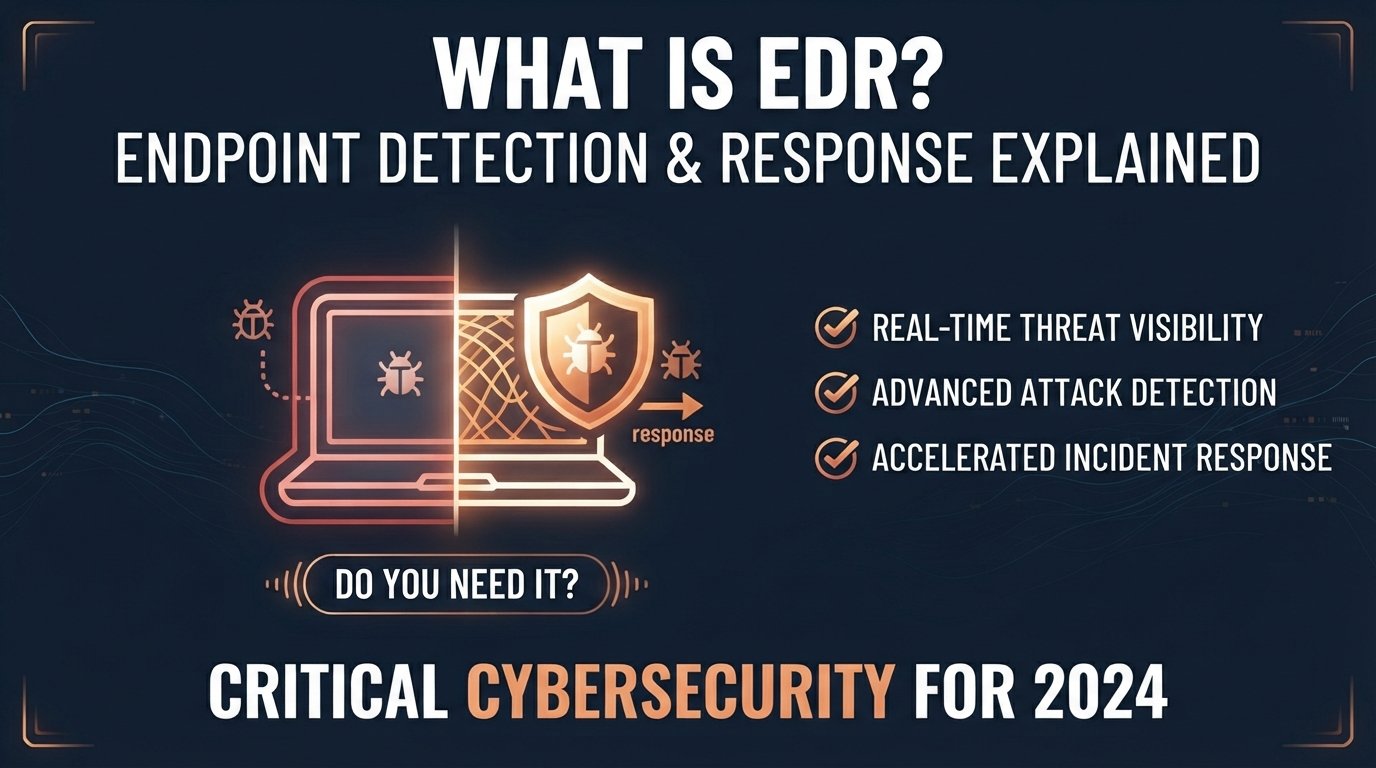
What Is EDR and Do You Need It?
Antivirus software has a fundamental blind spot: it mostly catches threats it already recognizes. EDR — endpoint detection and response — exists to catch the threats that don’t look like anything on a known list:
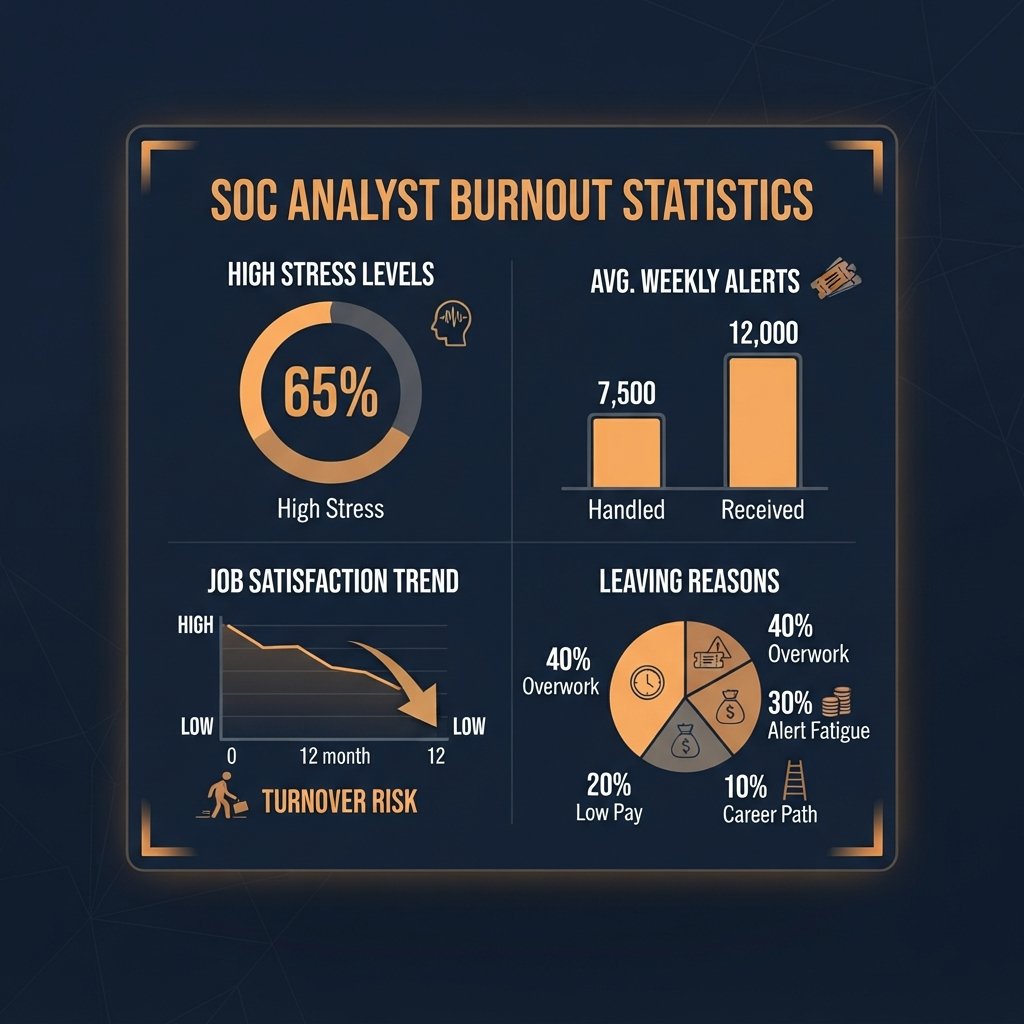
SOC Analyst Burnout Statistics
If you’re considering a SOC analyst role, or you’re already in one and wondering whether what you’re feeling is normal, the data has a clear answer
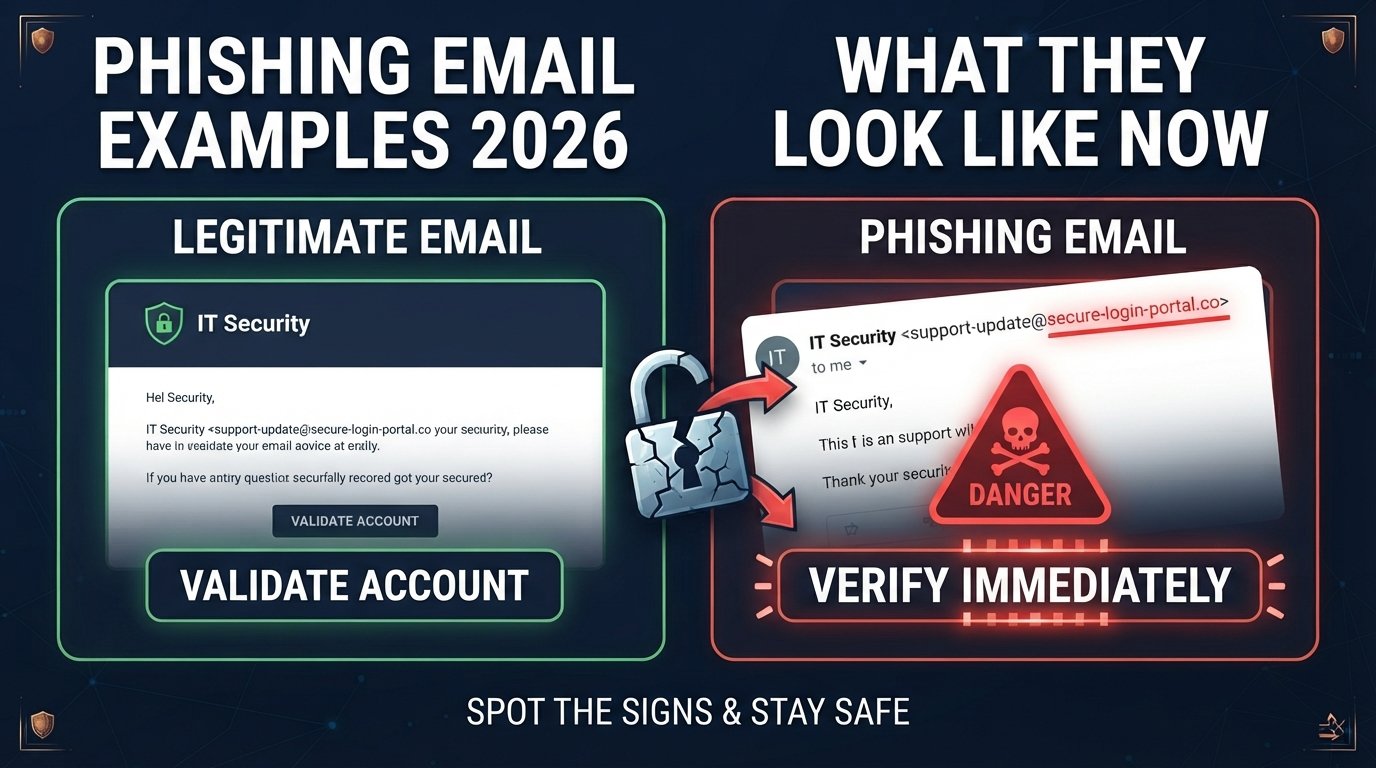
Phishing Email Examples 2026: What They Actually Look Like Now
The old advice for spotting a phishing email — bad grammar, a generic greeting, an obviously fake domain — doesn’t work anymore, and pretending it still does is actively dangerous.
Backup Strategy 101 for Small Business Owners
Most small business owners think they have a backup strategy. What they usually have is a folder that syncs to the cloud — which protects against a spilled coffee
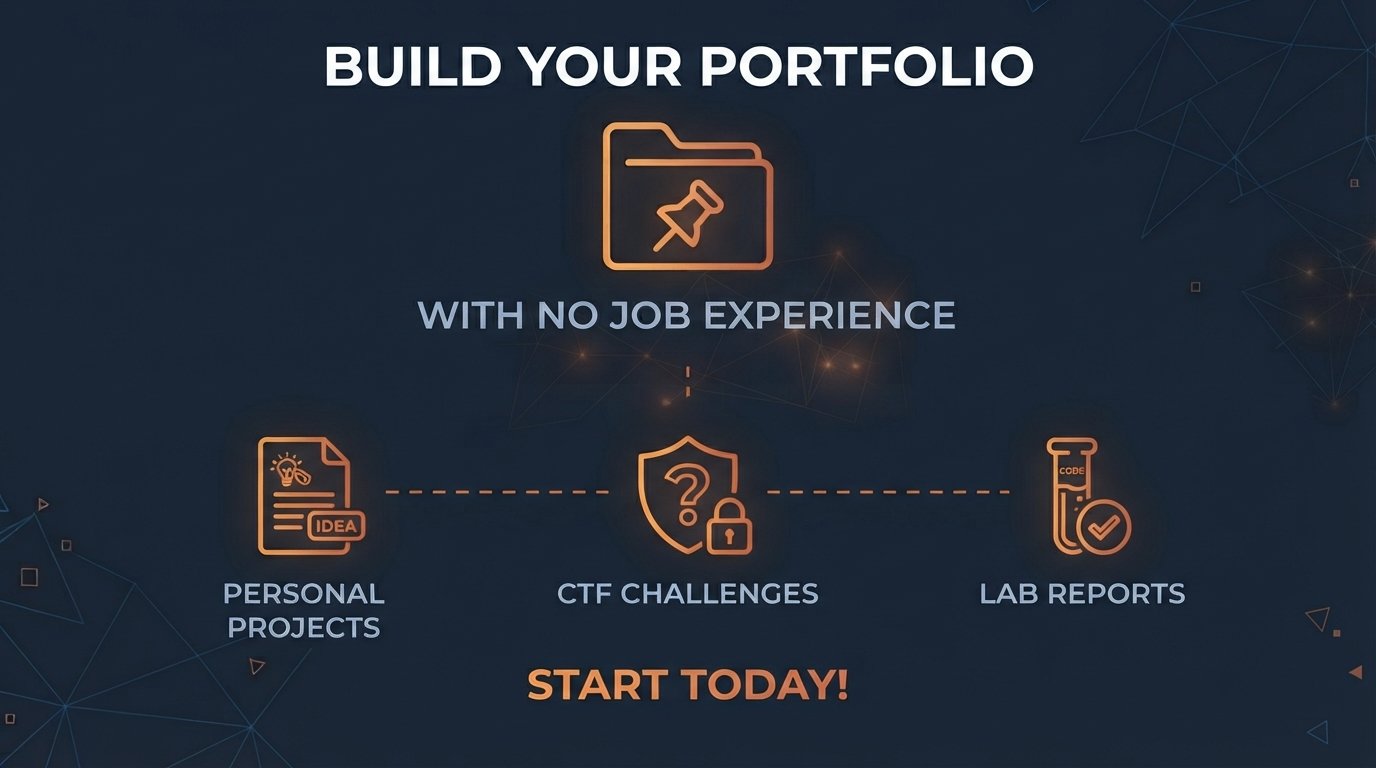
How to Build a Cybersecurity Portfolio With No Job Experience
Two candidates can apply for the same junior security role with nearly identical resumes — same certification, same bootcamp, same lack of formal job history
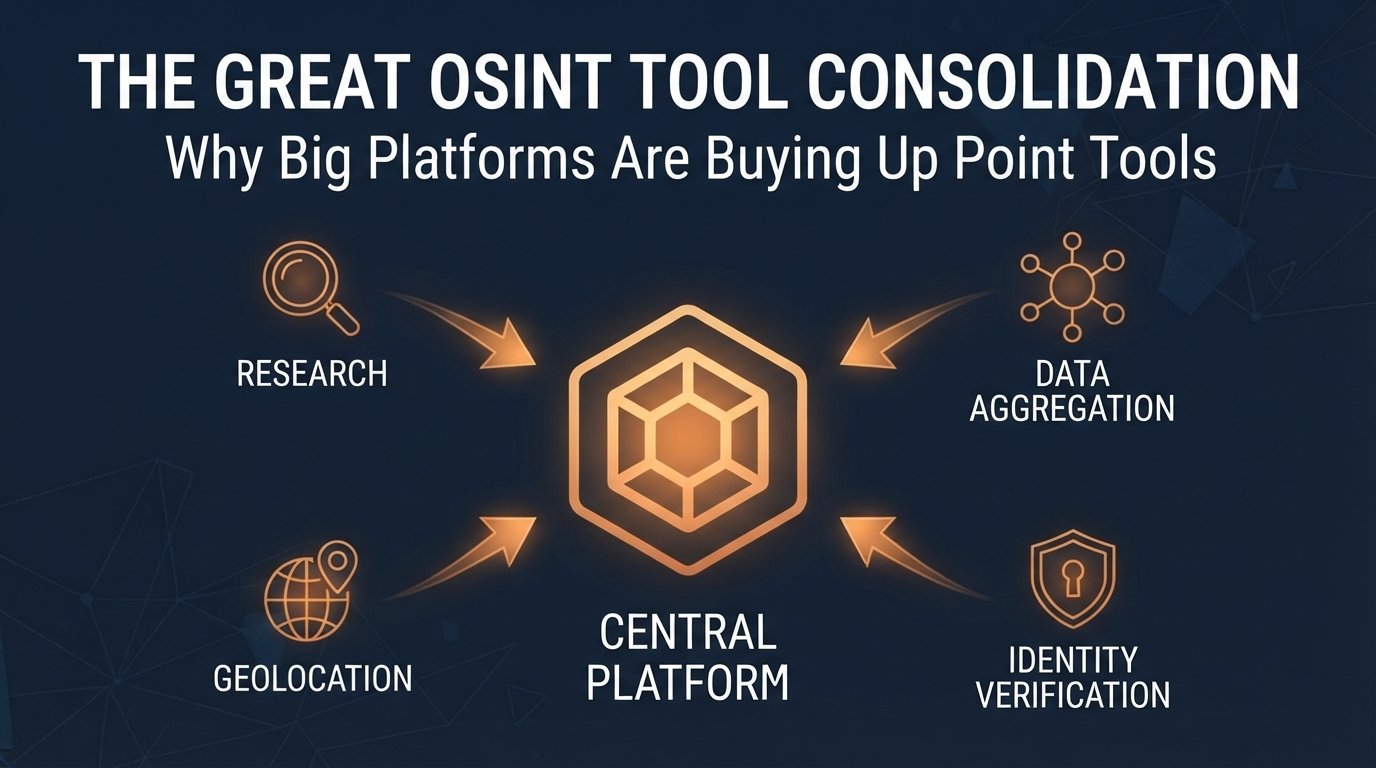
The Great OSINT Tool Consolidation: Why Big Platforms Are Buying Up Point Tools
Our post on the OSINT toolkit walked through 15 individual tools worth learning — each one built to do a specific job well. That landscape is changing underneath investigators’ feet.
GEOINT for Beginners: Using Satellite & Map Data in OSINT Investigations
A photo or video circulating online almost always comes with a claim attached: this happened here, at this time. GEOINT — geospatial intelligence — is the discipline
Recent Data Breach Analysis: Inside the McKesson Incident
Not every data breach makes for a useful case study — some are too vague, too unconfirmed, or too routine to teach much. But the incident disclosed
How to Store Backup Codes Safely
Not every data breach makes for a useful case study — some are too vague, too unconfirmed, or too routine to teach much. But the incident disclosed by McKesson
SOC Analyst Mistakes: The Habits That Quietly Hurt Detection
Nobody becomes a great SOC analyst by avoiding mistakes entirely — they become great by learning which mistakes actually matter and fixing the habits
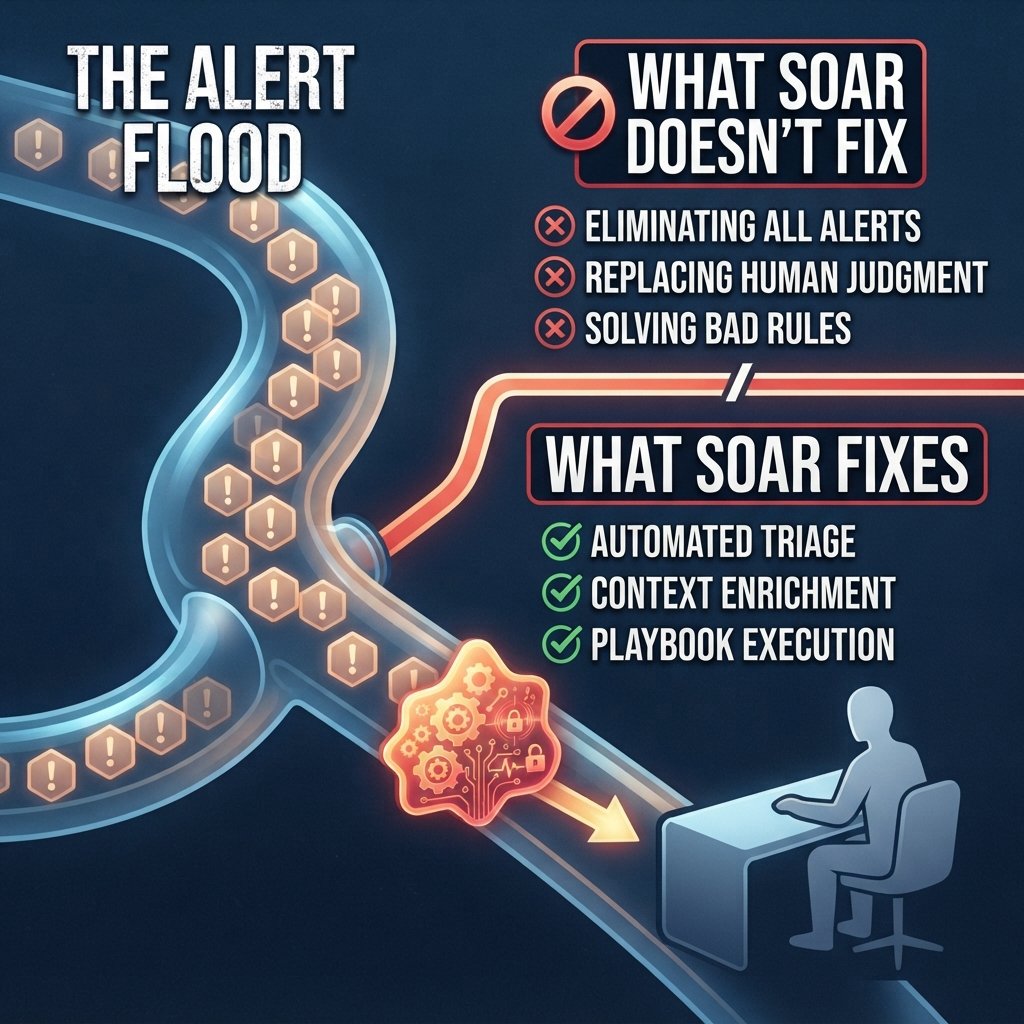
SOC Alert Automation: What SOAR Actually Does (and Doesn’t) Fix
Every SOC eventually hits the same wall: alert volume grows faster than headcount ever can. That’s the gap SOAR — Security Orchestration, Automation, and Response
10 Real Attacks a SOC Analyst Sees Every Single Day
Ask anyone who’s actually worked a SOC shift what their day looks like, and you’ll rarely hear about a single dramatic breach. The real story is quieter and more relentless
The First 15 Minutes of a Ransomware Attack: What We Actually Do
There’s a moment every SOC analyst knows — the split second between “this looks like a normal alert” and “this is ransomware.” Everything changes in that moment.
The OSINT Toolkit: 15 Tools Every Beginner Should Know
The OSINT tool landscape is enormous and growing fast — the global market for this kind of work is projected to grow roughly tenfold over the next decade.
Link Analysis Explained: How Investigators Map Relationships Between People, Accounts & Companies
A single record rarely tells you much on its own. A shell company registered in one country. A bank account in another. A name that shows up on a handful
Kids Online Safety: A Parent’s Quick Checklist
Keeping kids safe online doesn’t require becoming a tech expert or monitoring their every move. It mostly comes down to a handful of settings, habits, and conversations
How to Freeze Your Credit in 15 Minutes
If your information has ever shown up in a data breach — or even if it hasn’t — freezing your credit is one of the simplest, most effective, and completely
What to Do If Your Phone Is Stolen
Losing your phone to theft is stressful enough without also worrying about what someone could do with it. The good news: if you act quickly and in the right order, you can lock most attackers
Building Your First OSINT Monitoring Dashboard
Our last post covered why OSINT is shifting from search to stream — continuous monitoring instead of one-off queries. This one is the practical follow-up:
The Human-in-the-Loop Problem: Why OSINT Still Needs Analysts, Not Just AI
We’ve written before about how AI is automating the early stages of OSINT work — collection, entity resolution, pattern detection, all faster than any human analyst
From Searching to Streaming: How OSINT Monitoring Is Becoming Real-Time
For most of OSINT’s history, the basic workflow looked the same regardless of the tool: you ran a search, reviewed the results, and moved on until the next time you thought to check again.
CompTIA Security+ vs CEH: Which Should You Get First?
If you’re planning your first cybersecurity certification, you’ve almost certainly landed on this exact question. Both CompTIA Security+ and EC-Council’s Certified Ethical Hacker (CEH) show up constantly in “best certifications” lists
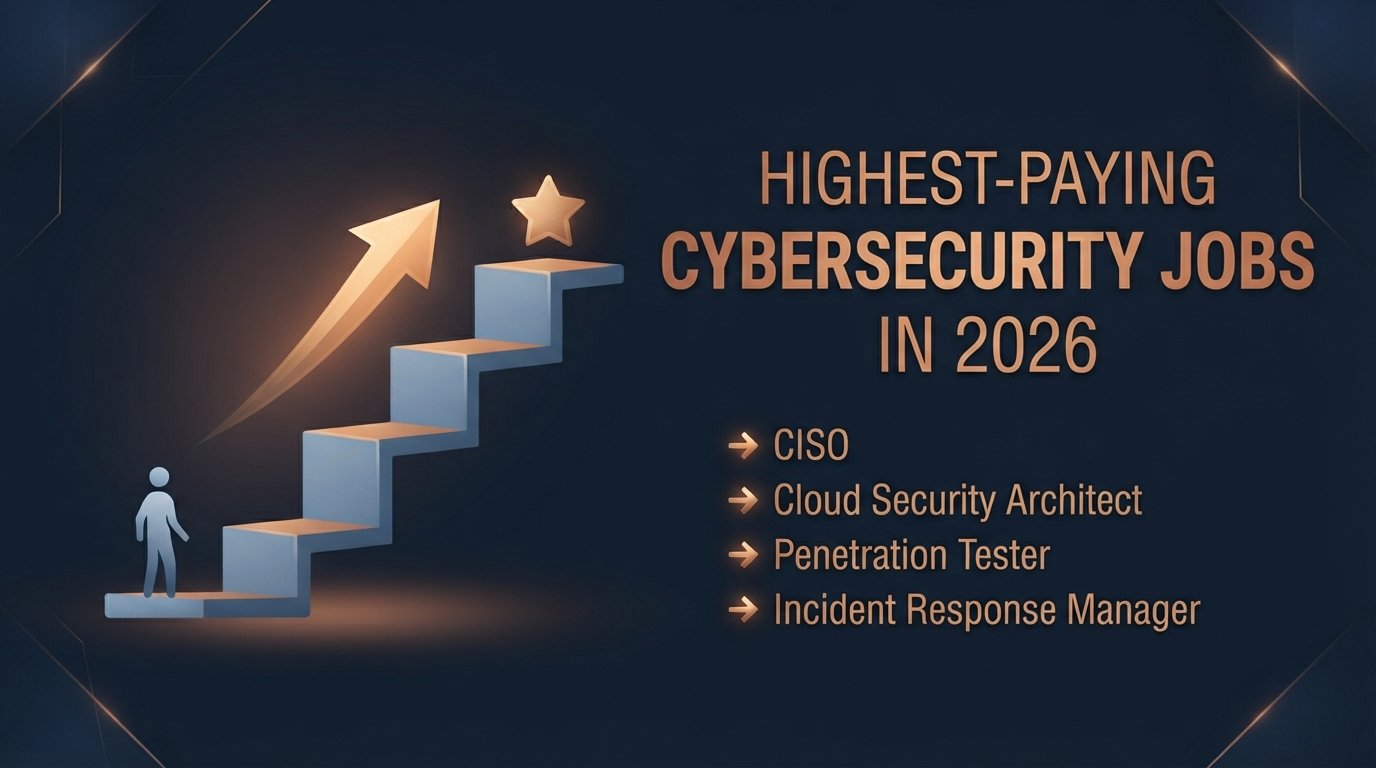
Highest-Paying Cybersecurity Jobs in 2026
Cybersecurity has become one of the more reliable paths to a high salary in tech, and the gap between entry-level and senior pay in this field is wider than in most other careers.
Is a Cybersecurity Career Right for You? Quick Quiz
Cybersecurity gets pitched constantly as the career to get into right now — and the numbers back that up. The Bureau of Labor Statistics projects roughly 33%
Maltego Explained: The Link-Analysis Tool Behind Modern OSINT Investigations
If you’ve spent any time researching OSINT tools, one name comes up more than almost any other: Maltego. It’s one of the most widely used investigation platforms
The Best OSINT Product Right Now: A 2026 Buyer’s Guide
Open-source intelligence (OSINT) has quietly become one of the fastest-growing corners of security and investigative work. Journalists, threat intel teams,
5 Free Tools to Spot AI-Generated Images and Video
Telling real media from AI-generated media by eye has gotten genuinely difficult. Tools like Sora, Veo, and Midjourney generate images and video convincing
Can You Trust That Voice? A Beginner’s Guide to Voice Clone Verification
For most of your life, hearing someone’s actual voice on the phone was about as close to proof of identity as you could get. That’s no longer true, and the shift
How to Spot a Business Email Compromise Scam
Business email compromise, or BEC, doesn’t look like the phishing attempts most people picture. There’s no obvious virus, no scary pop-up, no broken English
Do You Really Need Cyber Insurance? A Simple Guide
Cyber insurance used to be an easy thing to put off — a “someday” line item most small businesses never got around to. That’s changed. Attacks on small businesses
Employee Offboarding Checklist: Don’t Skip These Steps
When someone leaves your business, the exit interview and final paycheck get all the attention. What quietly gets missed is what happens to everything
How AI Is Automating Early-Stage OSINT Investigations
OSINT — open-source intelligence — means gathering information from publicly available sources: websites, social media, business filings, domain records,
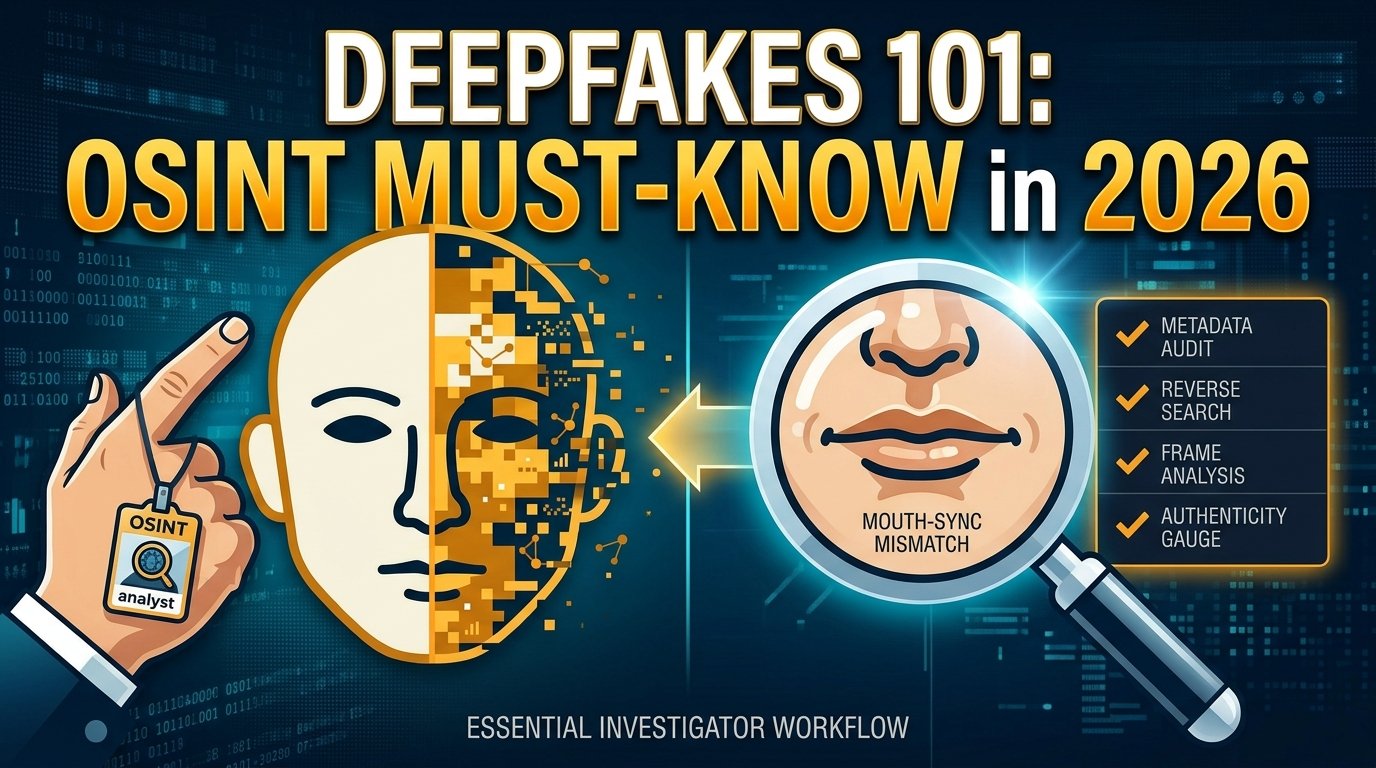
Deepfakes 101: What Every OSINT Investigator Needs to Know in 2026
Open-source intelligence has always rested on one basic assumption: that a photo, a video, or a voice recording is what it appears to be. That assumption
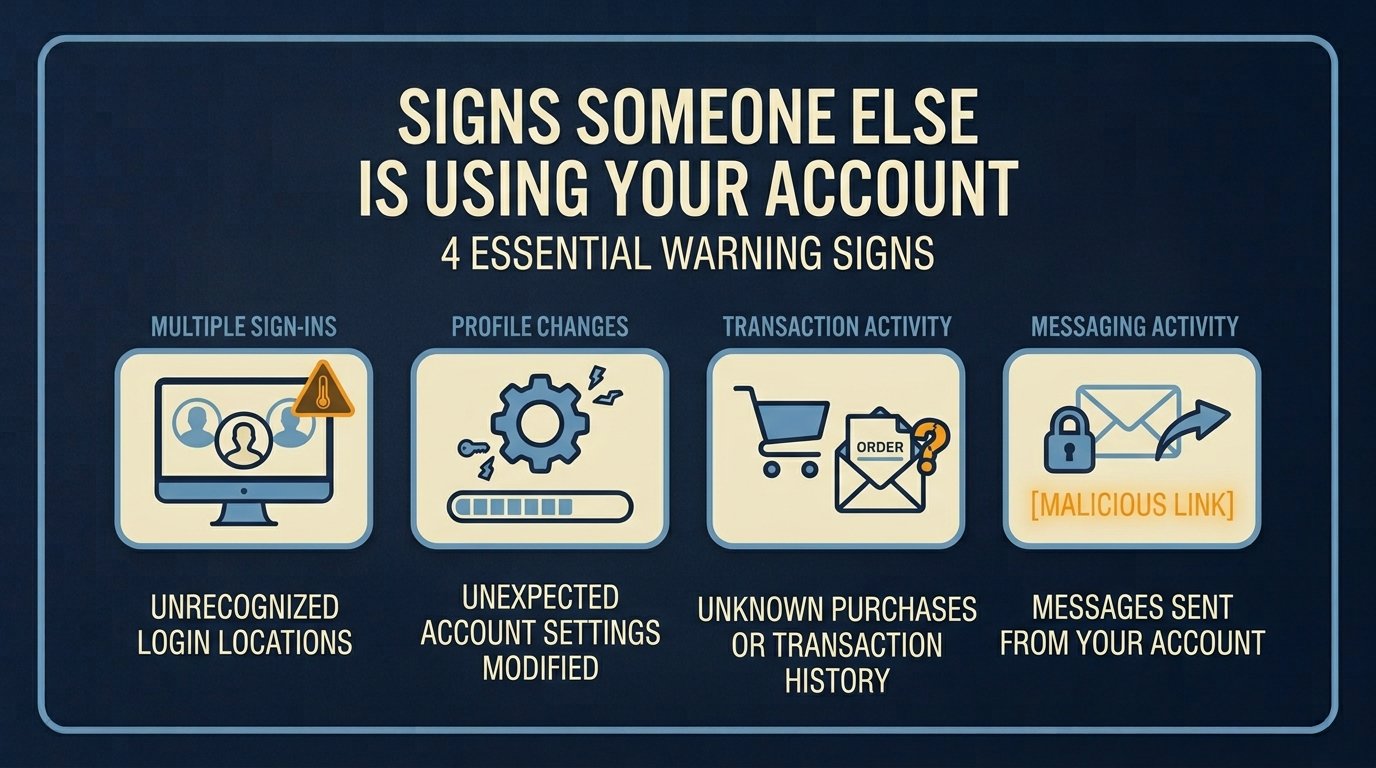
Signs Someone Else Is Using Your Account
Account takeovers rarely announce themselves. Nobody gets a pop-up saying “someone else is now using your email.” Instead, there’s usually a small trail of
How Often Should You Really Change Your Passwords?
For years, “change your password every 90 days” was treated as gospel. Plenty of businesses still enforce it, plenty of IT policies still require it,
Why OSINT Is Booming in 2026: Market Size, Drivers & What It Means for You
Open-source intelligence used to be a niche skill — something journalists, hobbyist investigators, and a handful of security analysts practiced quietly in the background.
AI in OSINT: Friend, Foe, or Both?
Ask ten OSINT professionals what they think of AI right now, and you’ll likely get ten nuanced answers — because AI in open-source intelligence isn’t a simple story.
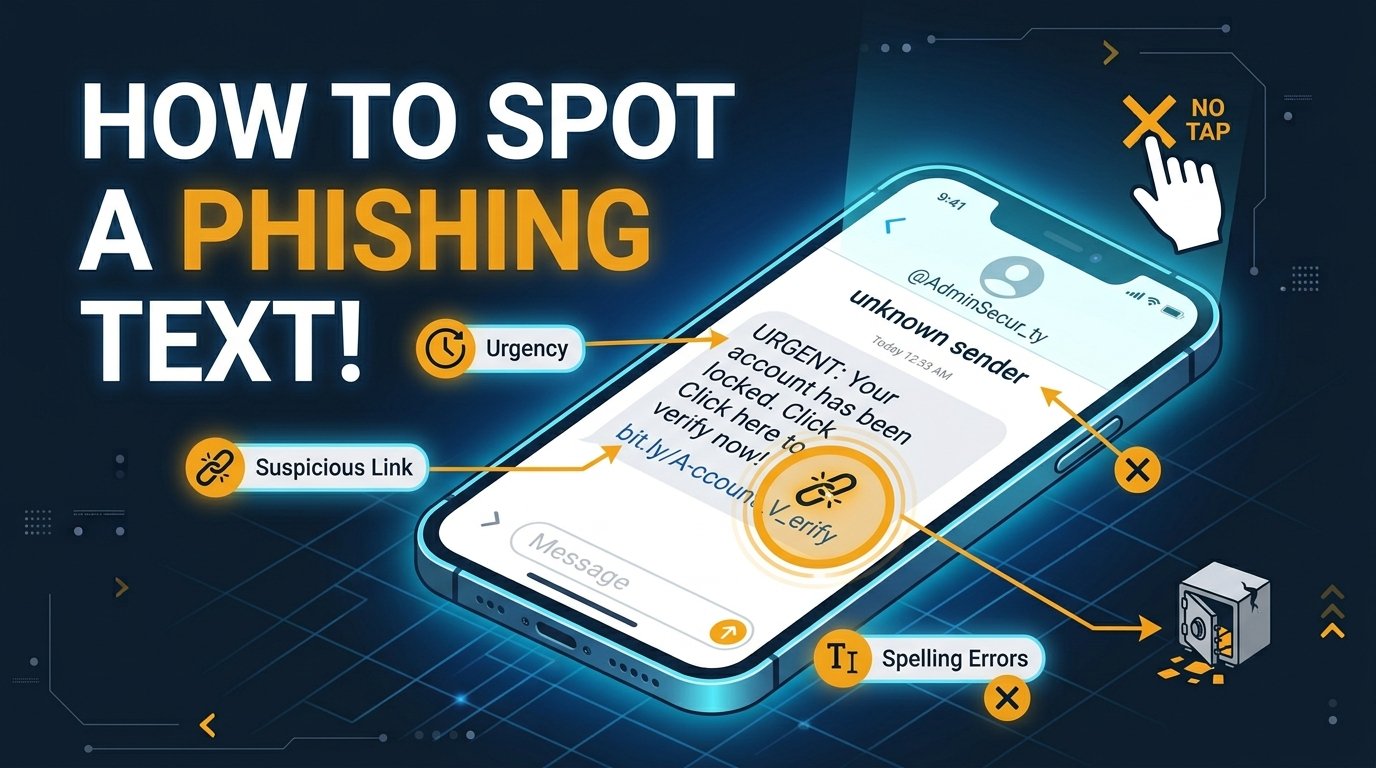
How to Spot a Phishing Text Message
Most cybersecurity advice focuses on email, and for good reason — but attackers have quietly shifted a lot of their effort to something people trust more and scrutinize less:
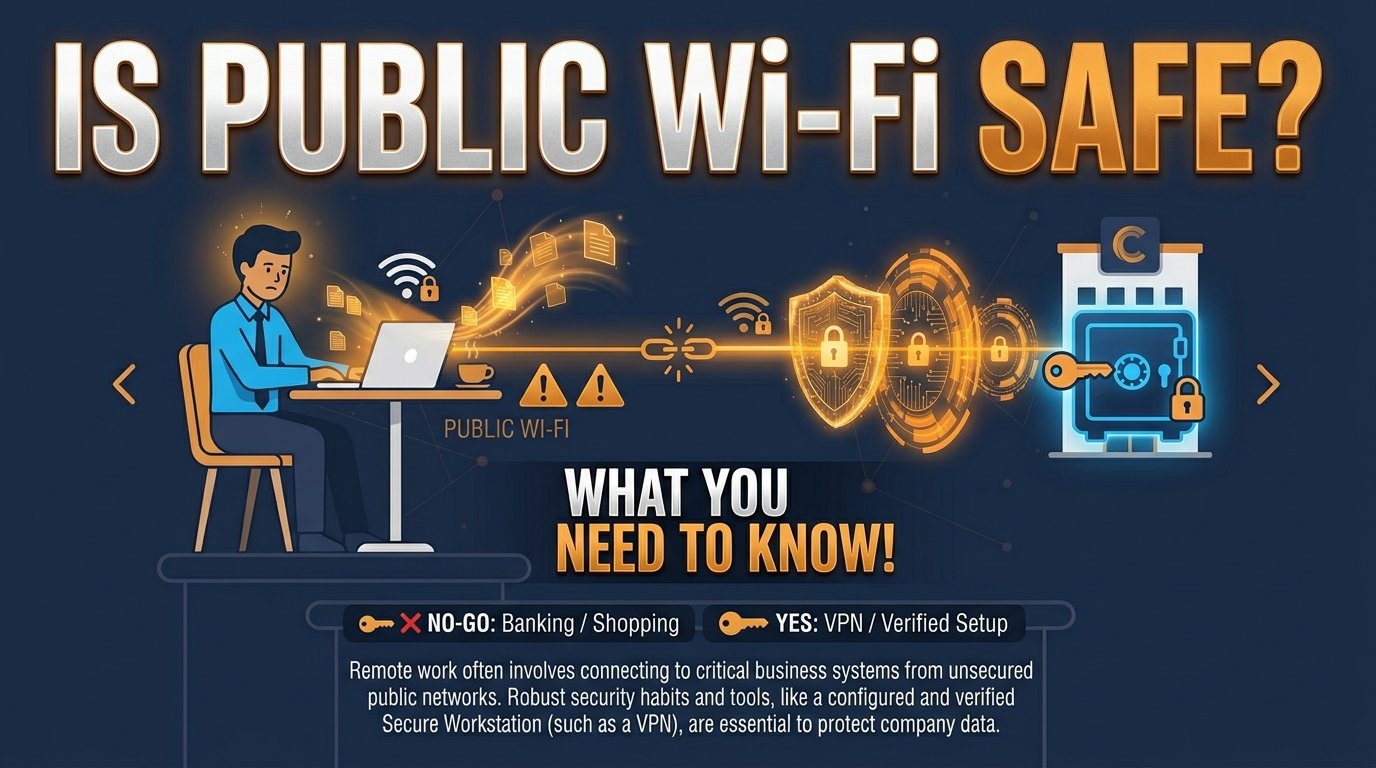
Is Public Wi-Fi Safe? What You Need to Know
If you’ve ever hesitated before connecting to the Wi-Fi at a coffee shop, hotel, or airport, you’ve probably heard some version of the same warning: don’t do it
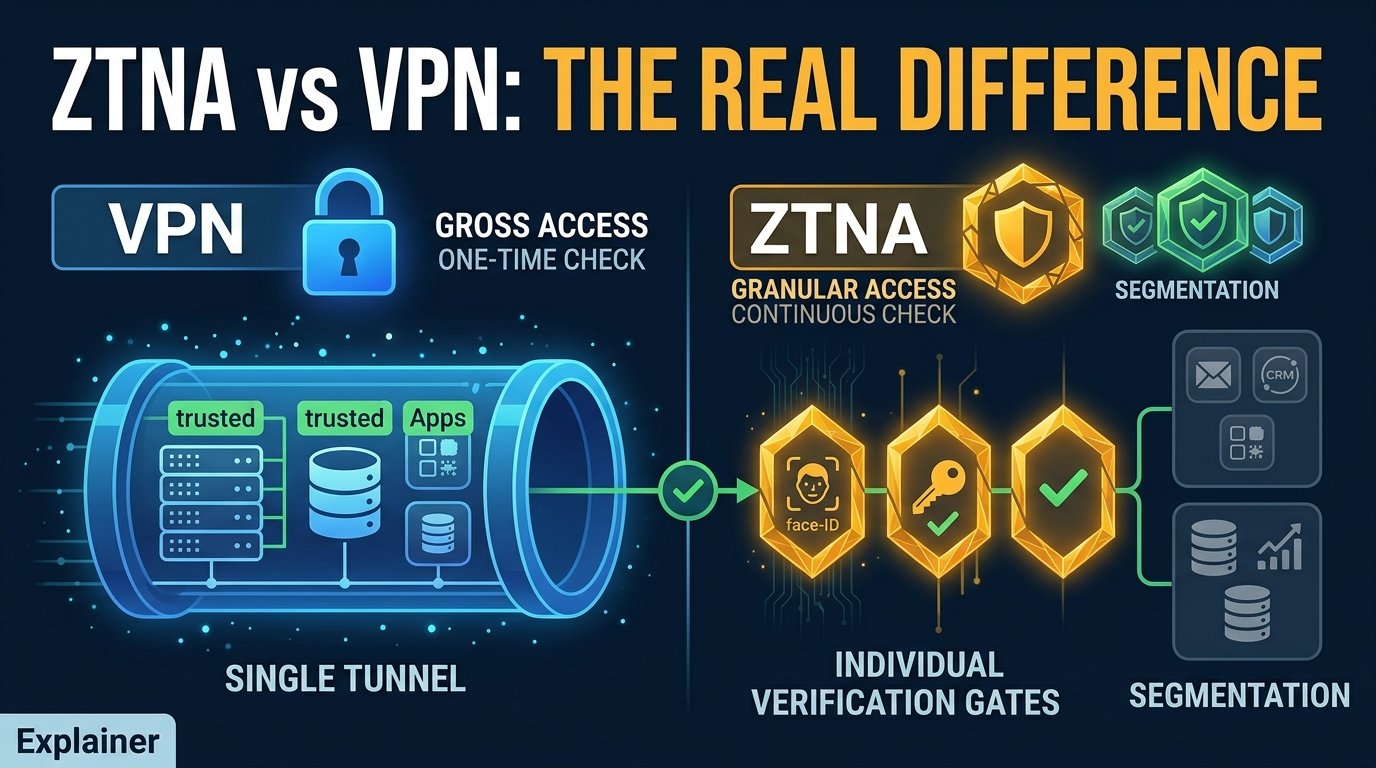
ZTNA vs VPN: What’s the Real Difference?
If your business uses a VPN so remote employees can log in, you’ve probably also started seeing a newer term floating around: ZTNA,
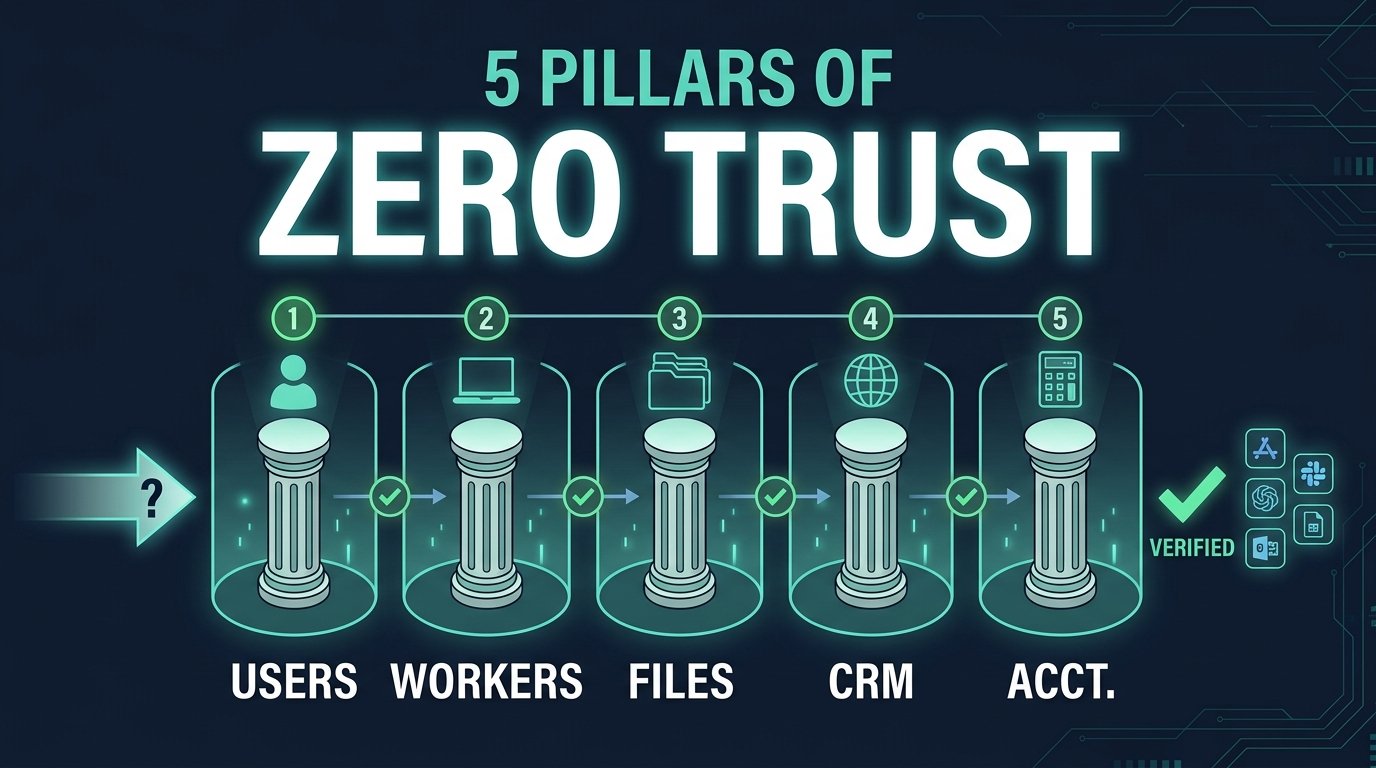
5 Pillars of a Zero Trust Framework
If you’ve read our earlier post on what Zero Trust actually means, you know the core idea: never trust access automatically, verify everything, every time.
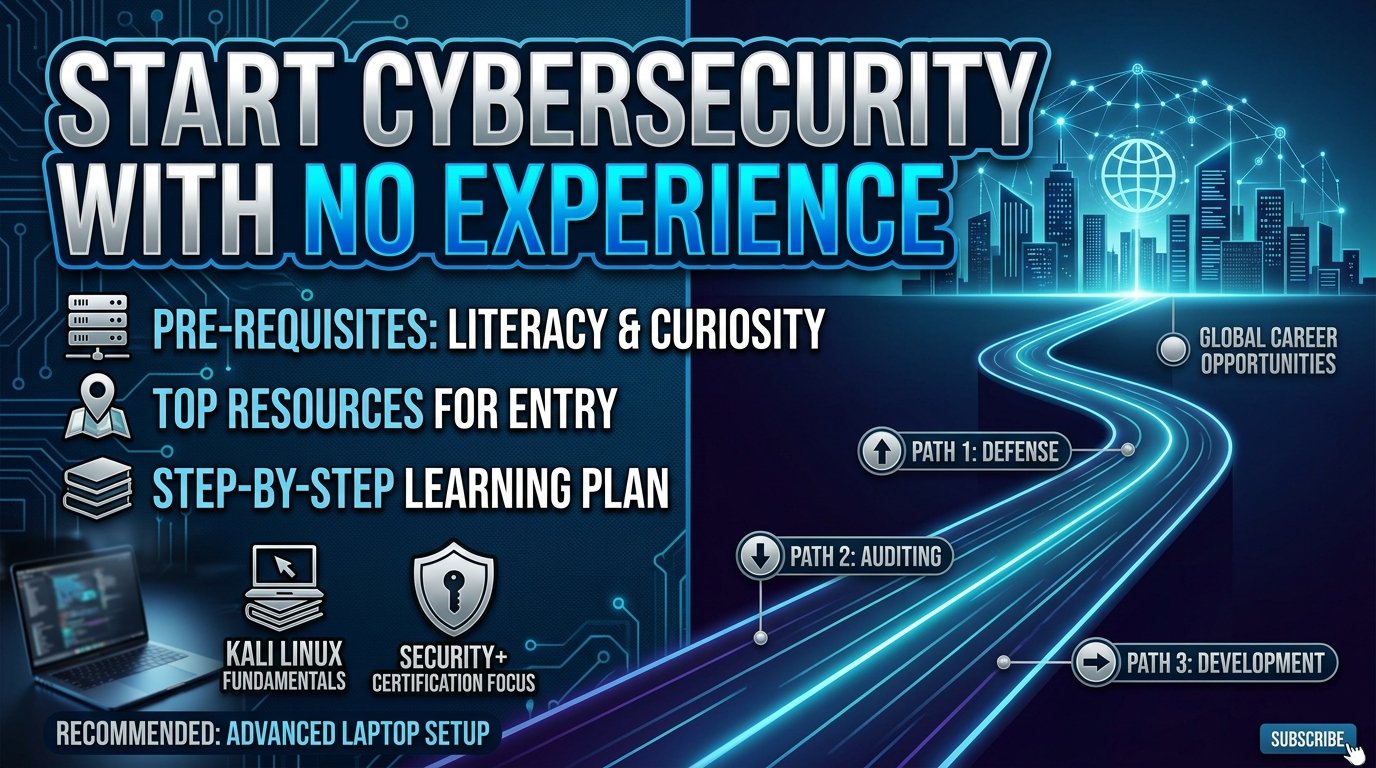
How to Start a Career in Cybersecurity With No Experience
Cybersecurity has a reputation problem. Scroll through job boards and you’ll see postings demanding five years of experience for an “entry-level” role, alphabet-soup…
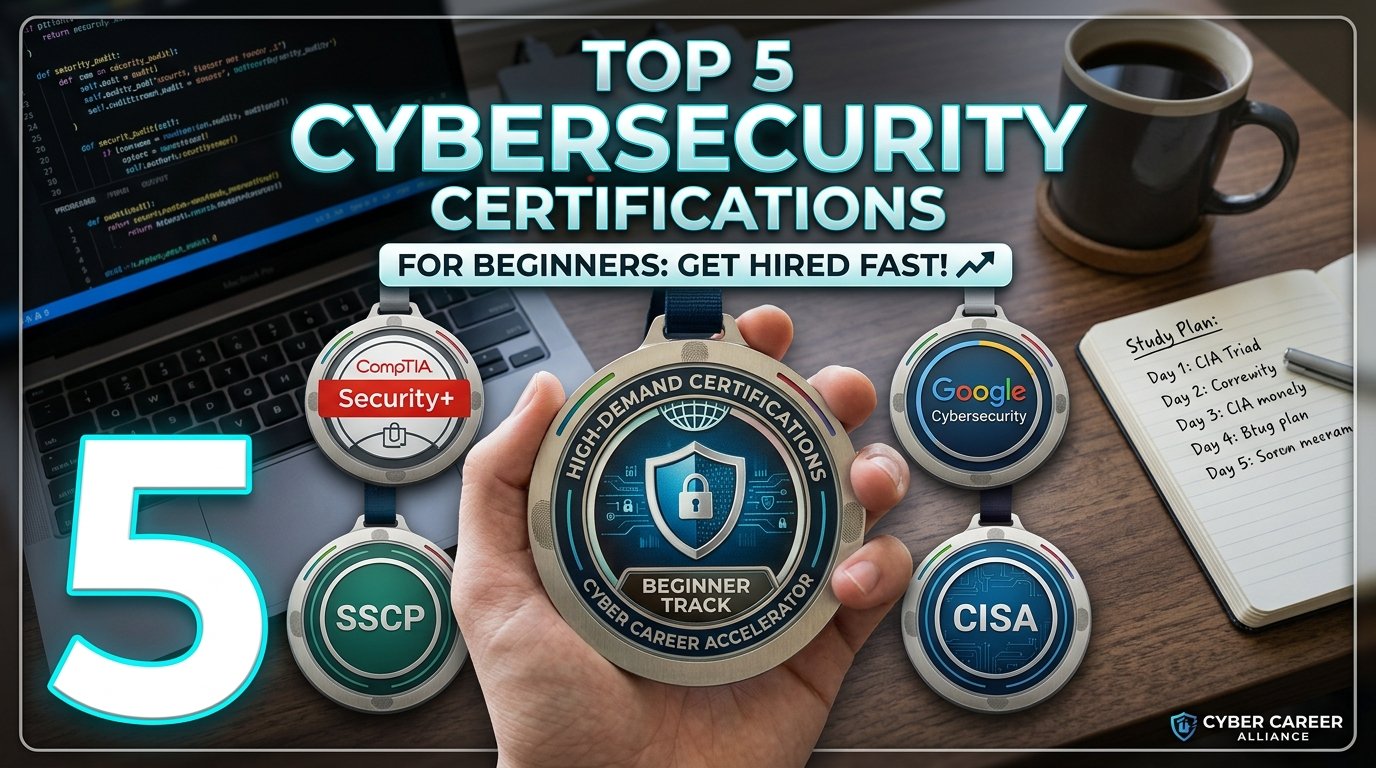
Top 5 Cybersecurity Certifications for Beginners
Walk into any cybersecurity subreddit or LinkedIn thread and you’ll find dozens of certifications thrown around — Security+, CEH, OSCP, CISSP, GSEC, CySA+.
Cybersecurity Career Roadmap: Beginner to Expert
Most “how to get into cybersecurity” advice stops at your first job. What happens after that is usually left vague — pick a specialty, keep learning, good luck
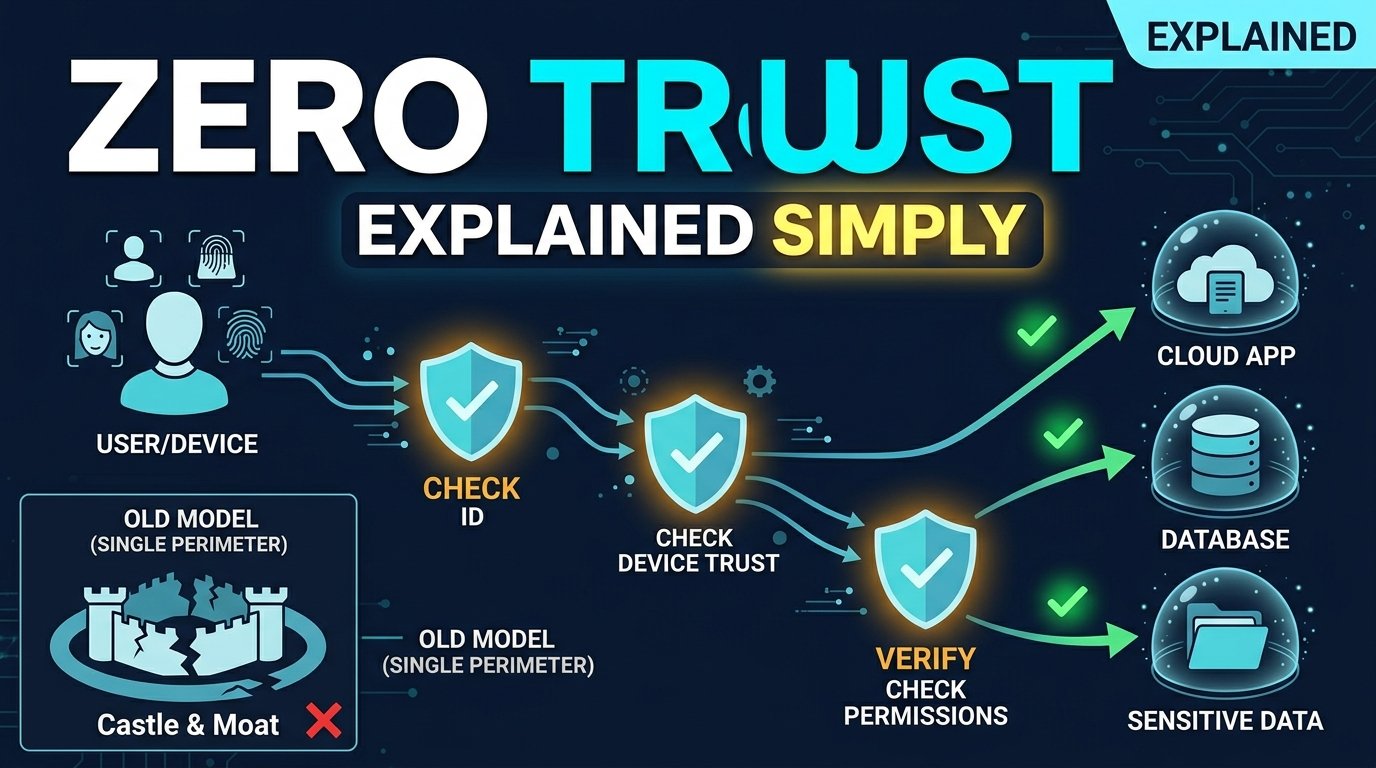
What Is Zero Trust? Explained Simply
If you’ve spent any time reading about cybersecurity lately, you’ve probably run into the term “Zero Trust.” It shows up in vendor pitches, security conference keynotes, and government guidance
5 AI Tools Hackers Are Using Right Now
There’s a quiet assumption a lot of people still make about hackers: that they’re lone geniuses hunched over a keyboard, painstakingly writing custom code line by line.
Your Smart Home Is Spying on You — Here’s Proof
Your smart speaker is listening. Your smart TV is tracking what you watch, down to the second. …
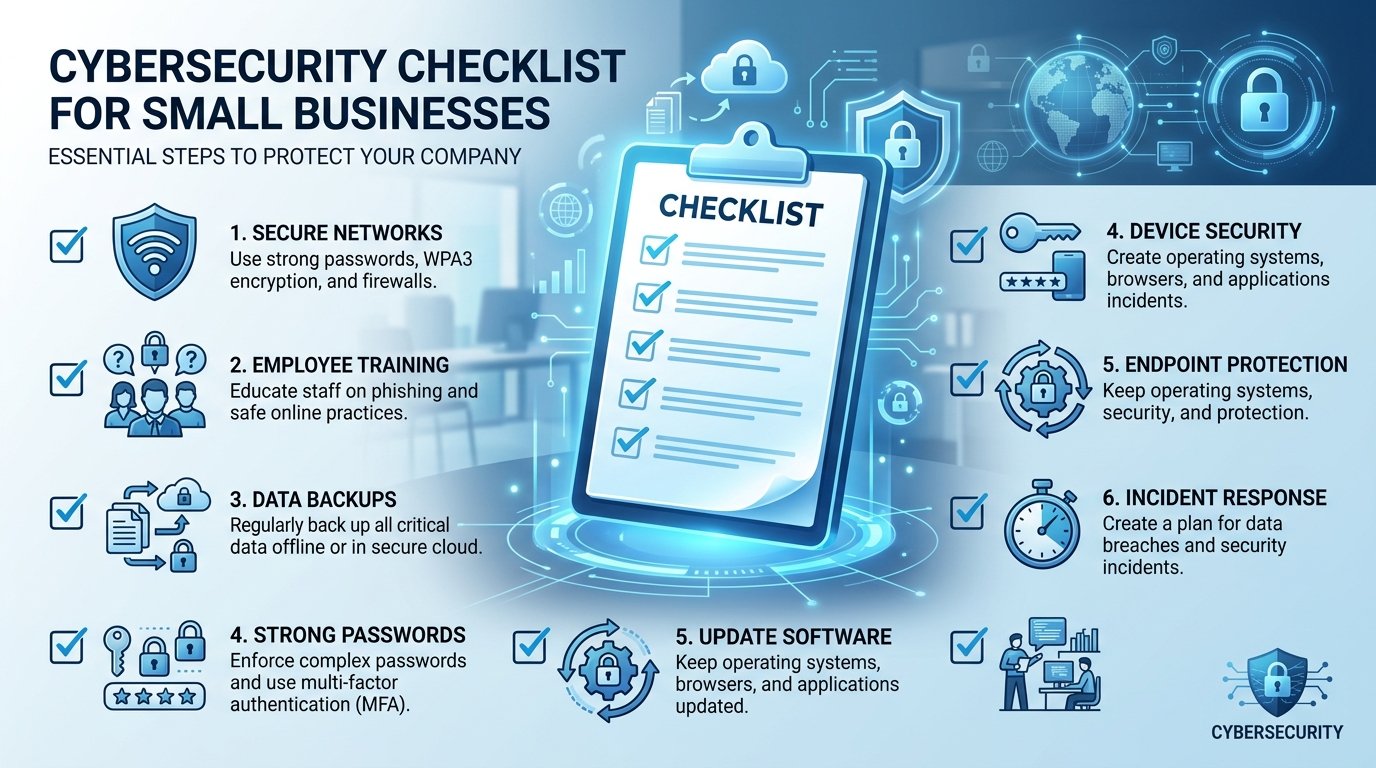
Cybersecurity Checklist for Small Businesses
If you run a small business, you’ve probably had the thought: “We’re too small for hackers to care about us.” That thought is exactly why small businesses get targeted so often…
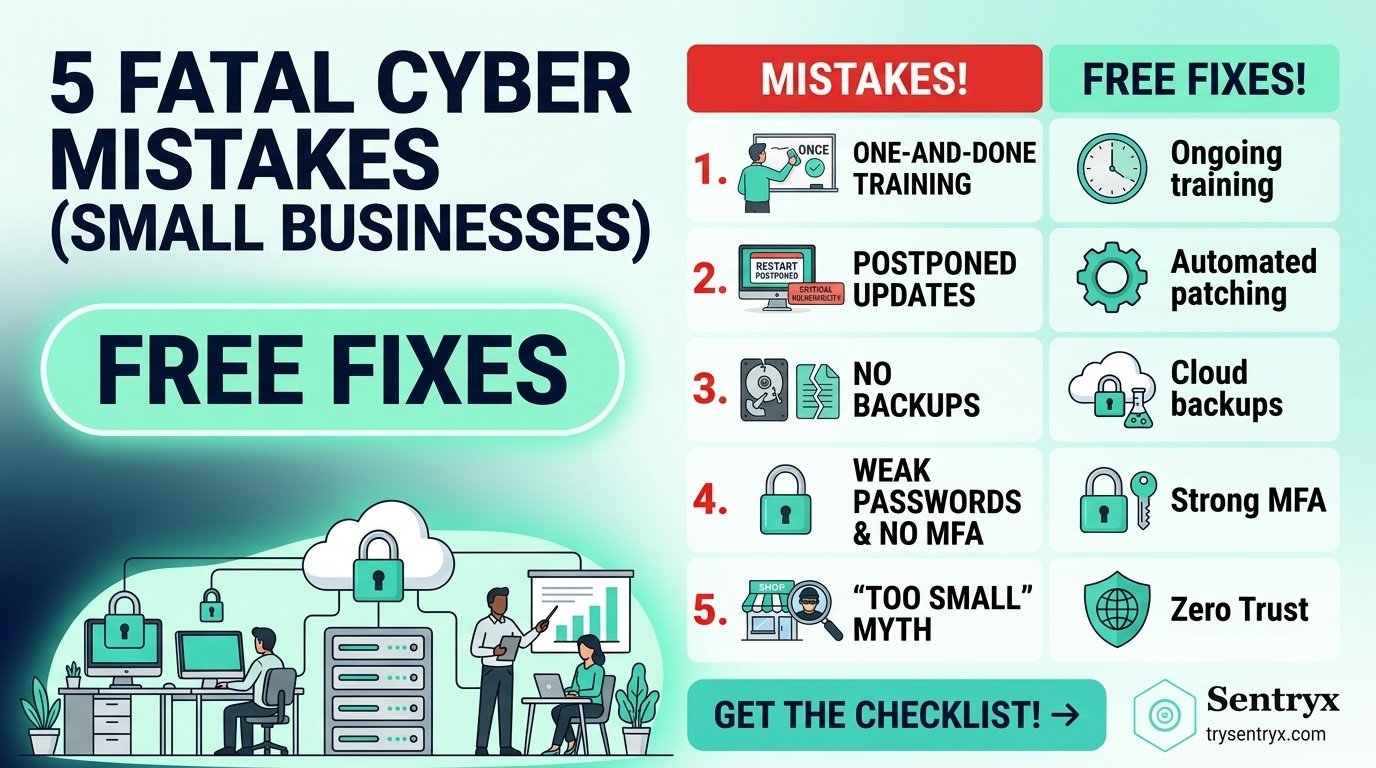
5 Costly Cybersecurity Mistakes Small Businesses Make (And How to Fix Them)
Small businesses often assume hackers only target big corporations. In reality, smaller companies are….

7 Cybersecurity Habits Every Smart Person Has
Discover 7 practical cybersecurity habits that actually protect your accounts and data — with step-by-step actions and trusted tools for…
Secure Your Home WiFi in 10 Minutes
Your home router is the front door to every device you own — your laptop, your phone, your smart TV, your kid’s tablet, even your smart doorbell. Most routers ship with weak default settings designed for easy setup, not security, which is exactly why they’re such a common target.
Best Password Managers in 2026: Free vs Paid
With automated cyberattacks escalating rapidly as we head into 2026, resting on default browser-saved credentials is no longer a safe option. True digital resilience requires dedicated end-to-end zero-knowledge encryption, comprehensive multi-device sync, and reliable secure sharing mechanics.
10 Signs Your Email Has Been Hacked (And What to Do)
Is your email account acting strange? From mysterious password reset requests to unexpected outbound messages, recognize the crucial warning signs that your inbox has been breached—and learn the immediate, step-by-step actions required to secure your data and reclaim control.
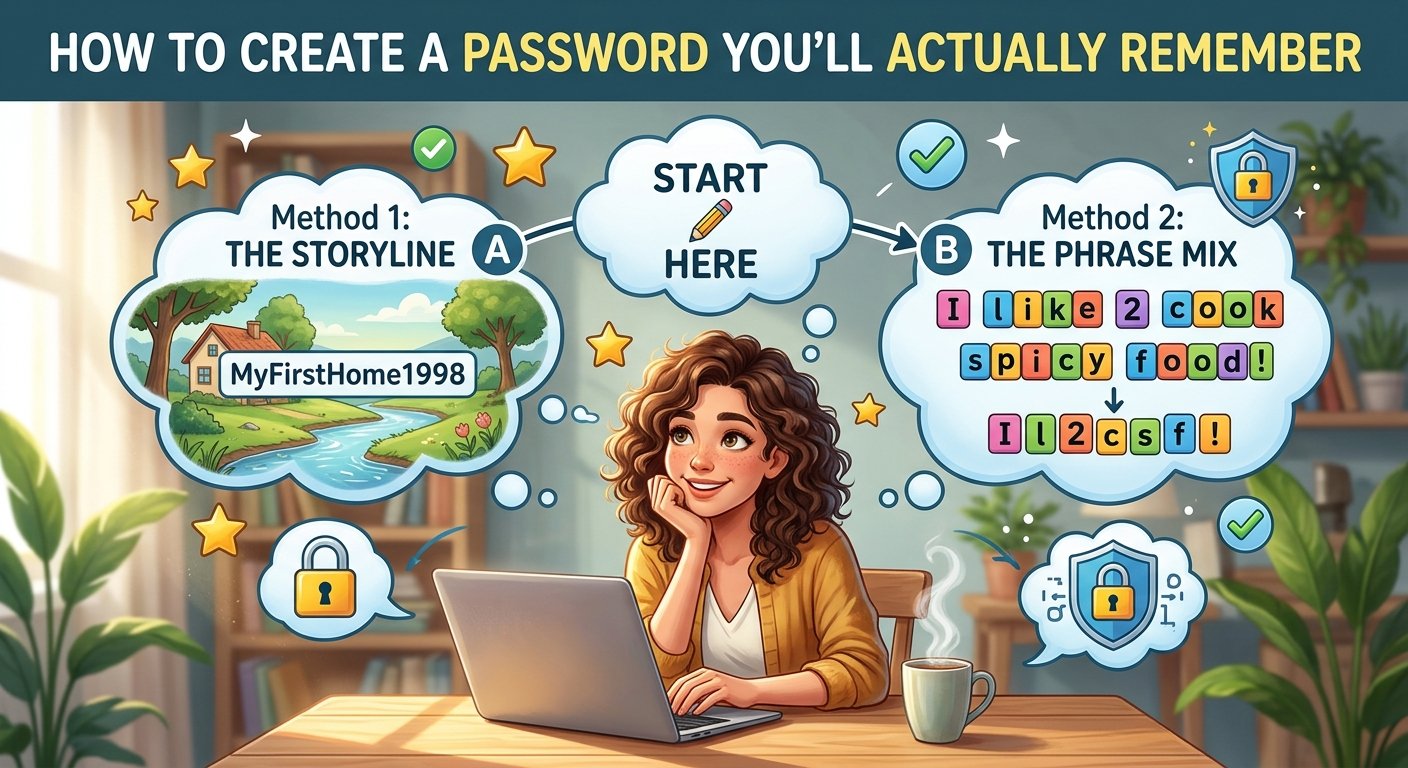
How to Create a Password You’ll Actually Remember
Let’s be honest: most password advice is written for robots, not people. “Use 12+ characters, uppercase, lowercase, a number, a symbol, and don’t write it down!” Sure — and then what? You forget it a week later,
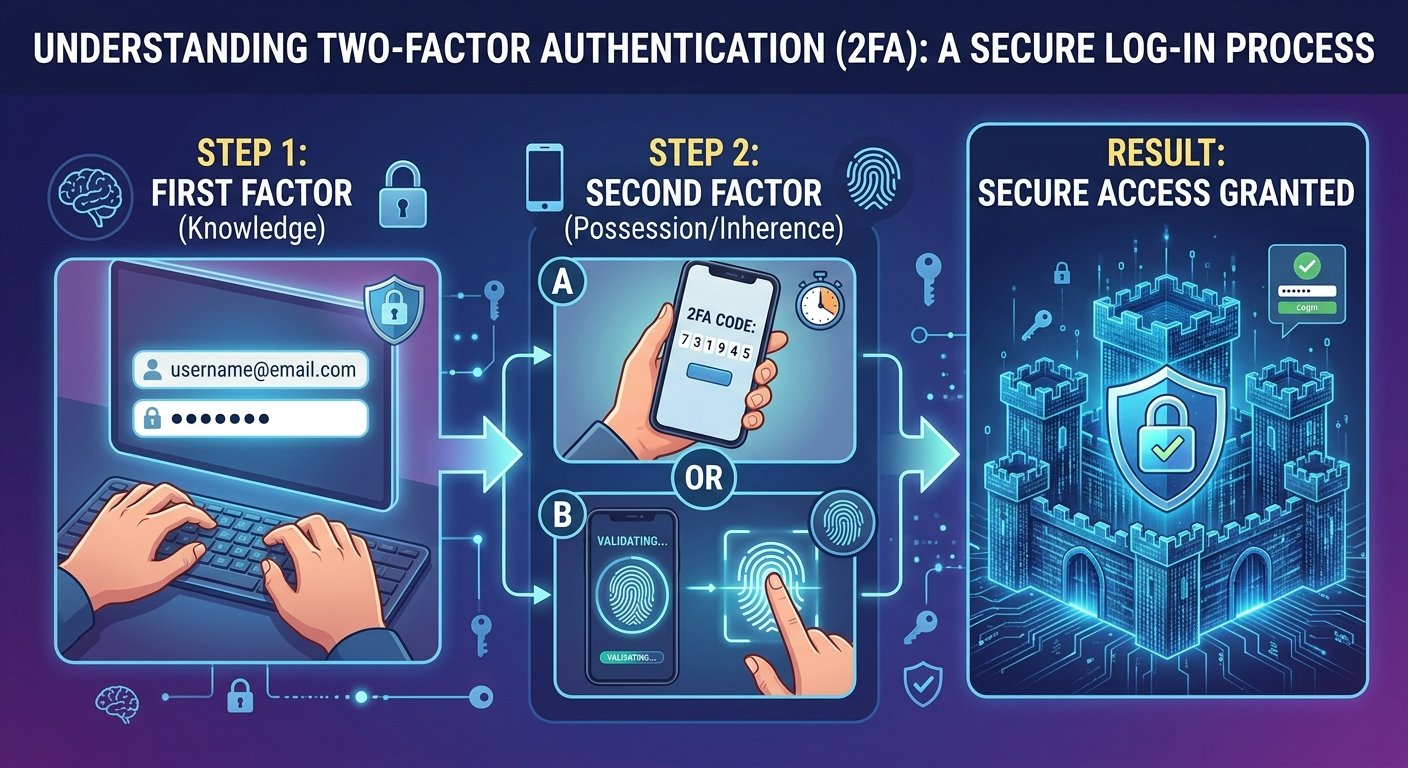
What Is Two-Factor Authentication?
You’ve probably seen it: you log into an account, and instead of getting in right away, you’re asked to enter a code that was just texted to your phone. Annoying? Maybe a little. But..
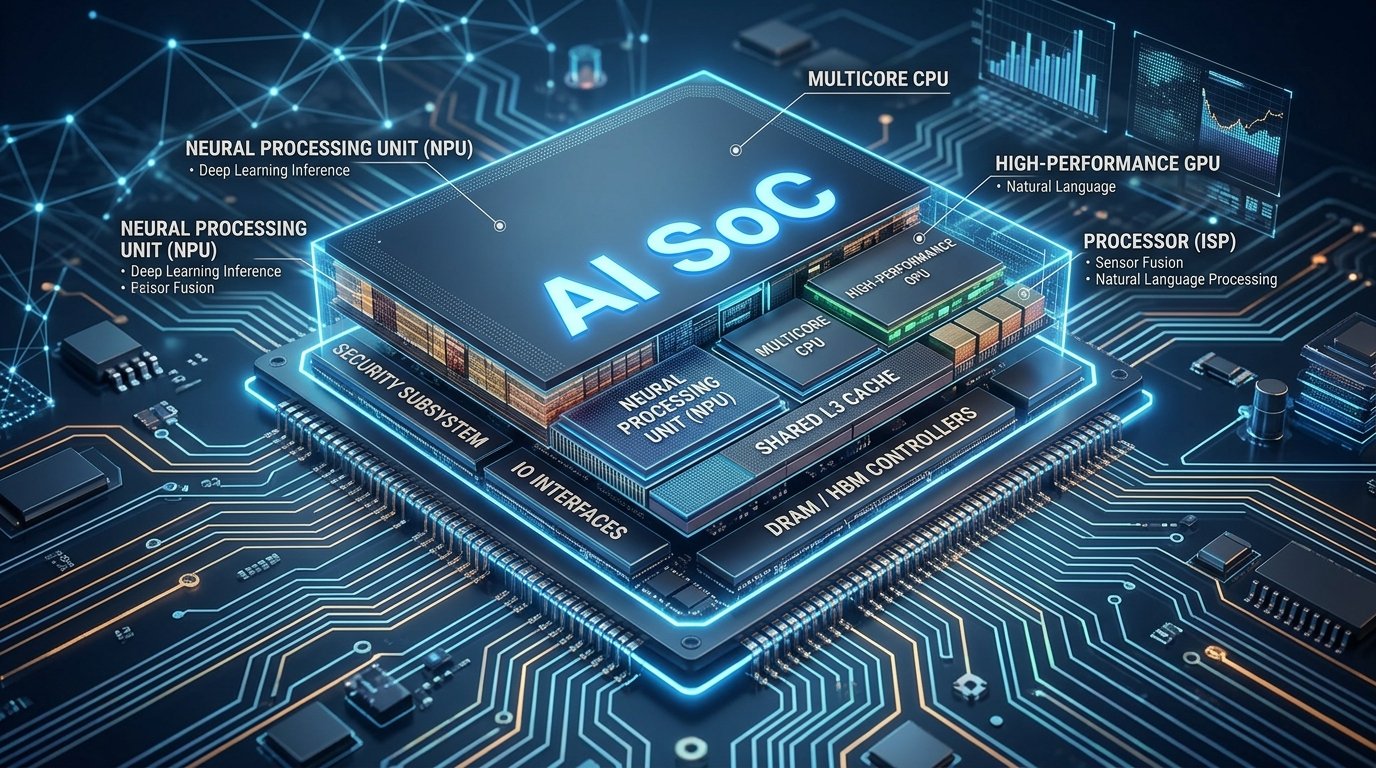
The AI-Powered SOC: Which Jobs Are Disappearing, and Which Are Growing
For years, the Security Operations Center was the nerve center of cyber defense, rows of analysts staring at dashboards, triaging alerts, and chasing down every red flag before it turned into a breach. That model is changing fast.
Deepfake Scams Are Draining Bank Accounts — Here’s How to Spot One
Picture this: your finance manager gets a video call from the CEO. Same face. Same voice. Same way he always clears his throat before saying something important. He needs an urgent wire transfer approved, a big one, before the market closes. So she approves it.
ChatGPT Is Writing Malware Now — Should You Be Worried?
A few years ago, writing malware took real skill. You needed to understand programming, operating systems, and how to slip past antivirus software, a barrier that kept a lot of would-be attackers out of the game entirely.
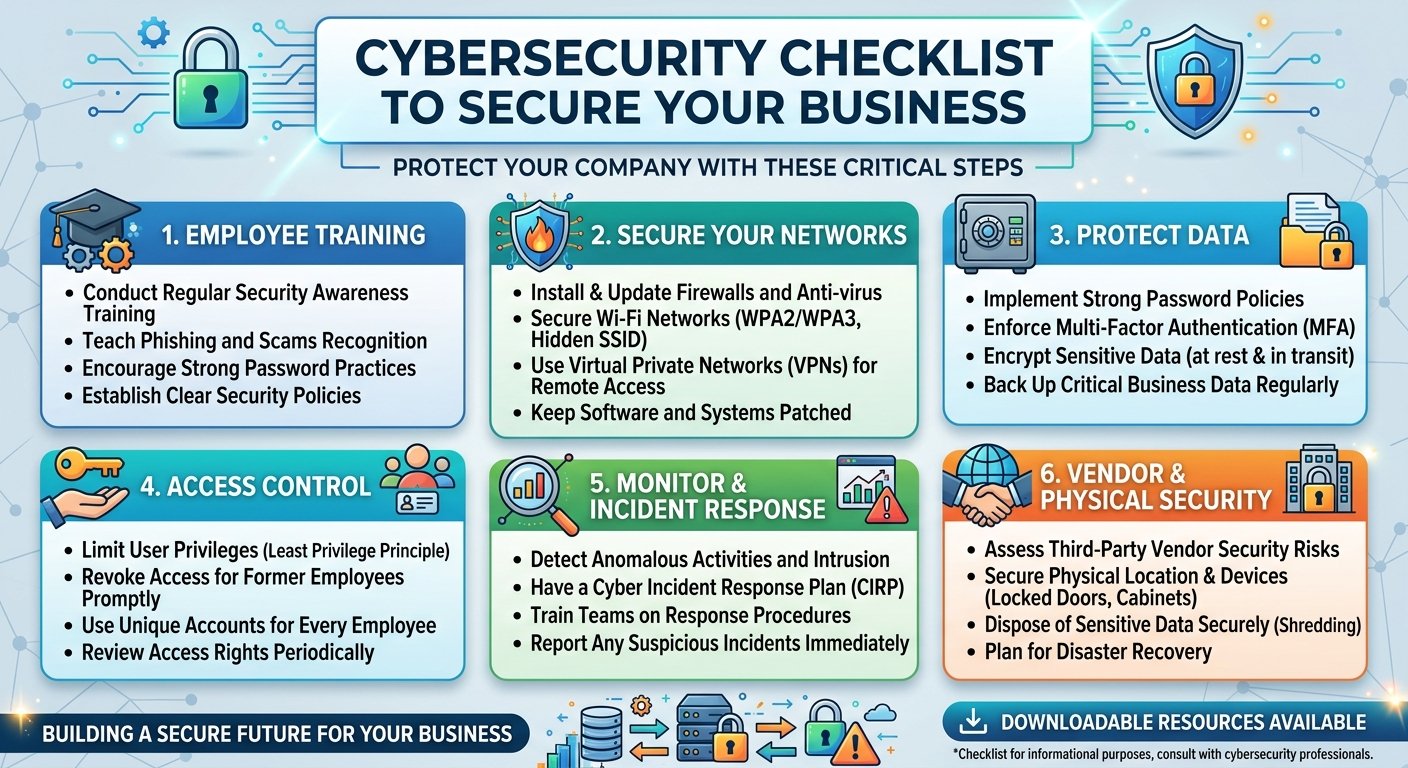
How Much Does a Data Breach Actually Cost a Small Business?
Every year, a headline number makes the rounds: the average data breach now costs millions of dollars. It’s meant to grab attention, and it does .
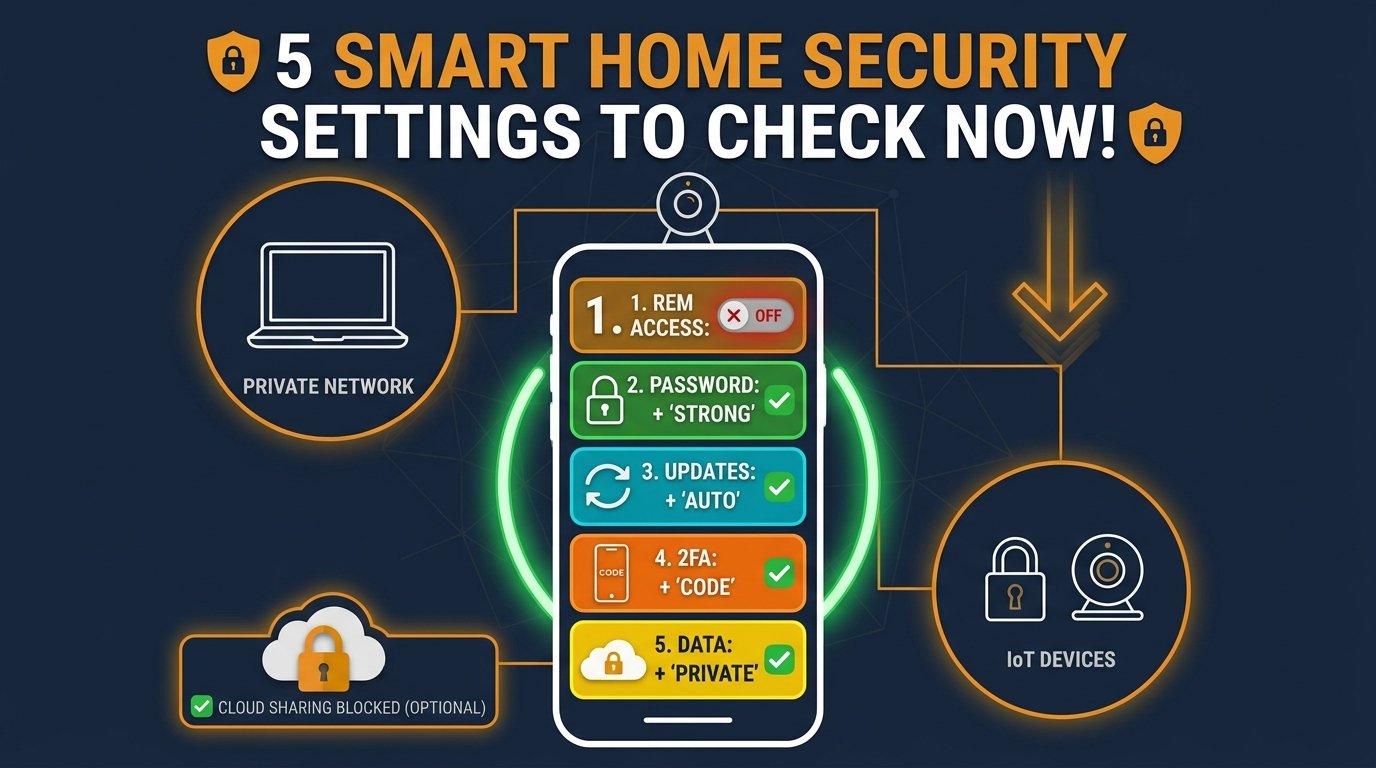
Smart Home Devices: 5 Security Settings to Check Today
Smart cameras, doorbells, thermostats, locks, and speakers have quietly become a normal part of most homes — and for small business owners, sometimes the office too.
Passkeys Explained: The Future of Login
You’ve probably already used a passkey without fully realizing what it was. If you’ve ever unlocked a login screen with your face or fingerprint instead of typing a password,