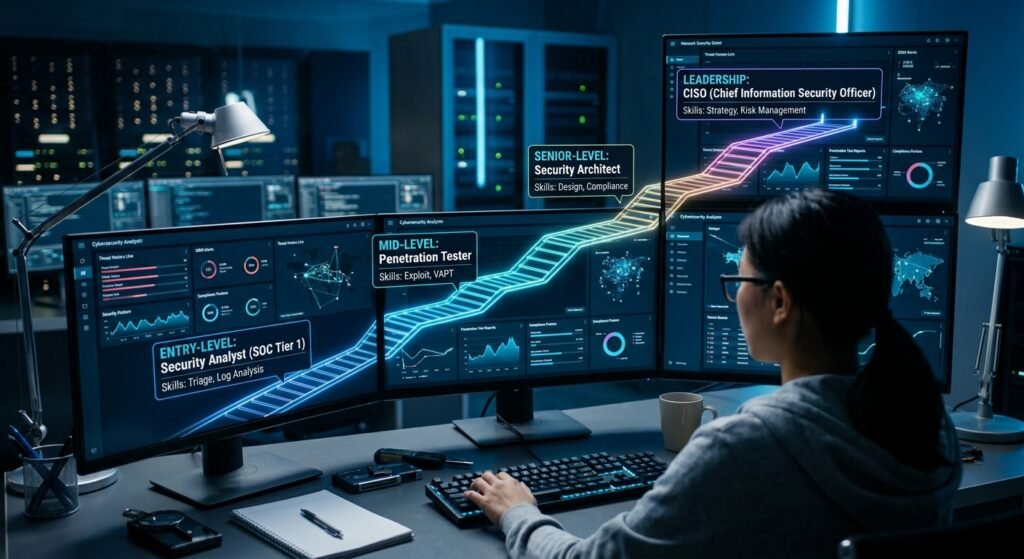
Most “how to get into cybersecurity” advice stops at your first job. What happens after that is usually left vague — pick a specialty, keep learning, good luck. That gap causes a lot of stalled careers: people land a SOC analyst role and then have no idea what the next five, ten, or fifteen years should actually look like.
This roadmap covers the whole arc — from someone who has never touched a terminal to a senior practitioner running a security function. Nobody moves through these stages at exactly the same pace, and the paths branch heavily after the entry level. Treat this as a map, not a fixed timeline.
Stage 1: Foundations (0–6 months)
Goal: Build the baseline knowledge every security role assumes you have.
Before you can specialize in anything, you need to understand how systems and networks actually work. This stage is unglamorous and easy to rush — don’t.
- Networking — IP addressing, DNS, firewalls, how traffic actually moves
- Operating systems — comfort in both Windows and Linux, including the command line
- How the web works — HTTP/HTTPS, client-server requests, basic scripting (Python or Bash)
Certifications at this stage: CompTIA Network+ if your networking is shaky, or go straight into CompTIA Security+ or the Google Cybersecurity Certificate if you’re comfortable with the fundamentals already.
What “done” looks like: You can explain how a request travels from a browser to a server and back, navigate a Linux terminal without panicking, and you’ve built a basic home lab.
Stage 2: Breaking In (6 months – 2 years)
Goal: Land your first role and build real-world instincts that no course can teach.
This is where most beginners get stuck, because the jump from “studied the fundamentals” to “hired” requires evidence, not just knowledge. Two things close that gap: hands-on practice and a visible portfolio.
- Hands-on labs — TryHackMe, Hack The Box, or a self-built virtual lab practicing both attack and defense
- A portfolio — write-ups of labs completed, a GitHub with scripts and notes, consistent LinkedIn posts about what you’re learning
- Typical entry roles: SOC Analyst (Tier 1), IT Support/Help Desk with a security focus, Junior GRC Analyst, Security Awareness Coordinator
Most people spend one to two years here before moving up or specializing. The single biggest skill developed at this stage isn’t technical — it’s learning to triage: what’s actually a threat, what’s noise, and how to communicate that clearly under pressure.
Certifications to add: CompTIA Security+ (if not already done), CompTIA CySA+ if you’re leaning toward SOC/blue-team work.
Stage 3: Choosing a Specialization (2–5 years)
Goal: Move from generalist to specialist. This is the branching point of the entire career.
By now you’ve seen enough of the field to know what actually interests you. Cybersecurity splits into distinct tracks, and while people do move between them, each has its own skill ladder:
Offensive security (penetration testing / red team)
- Focus: finding and exploiting vulnerabilities before attackers do
- Core skills: web app testing, network exploitation, scripting, report writing
- Certifications: OSCP (widely considered the credential that actually proves hands-on skill), eJPT as an earlier step
Defensive security (blue team / incident response)
- Focus: detecting, containing, and recovering from attacks
- Core skills: SIEM tools, log analysis, malware triage, forensics fundamentals
- Certifications: GCIH, CompTIA CySA+, Blue Team Level 1 (BTL1)
Governance, risk, and compliance (GRC)
- Focus: policy, risk assessment, audits, regulatory frameworks (ISO 27001, SOC 2, NIST)
- Core skills: risk frameworks, communication with non-technical stakeholders, audit processes
- Certifications: CISA, CRISC (both typically require some years of experience to fully certify)
Cloud security
- Focus: securing AWS/Azure/GCP environments, identity and access management at scale
- Core skills: cloud architecture, IAM, infrastructure-as-code security
- Certifications: AWS Certified Security – Specialty, Azure Security Engineer Associate
Application security
- Focus: finding and fixing vulnerabilities in software before it ships
- Core skills: secure coding practices, code review, SAST/DAST tooling
- Certifications: GWAPT, or a strong portfolio of bug bounty findings often carries more weight than a cert here
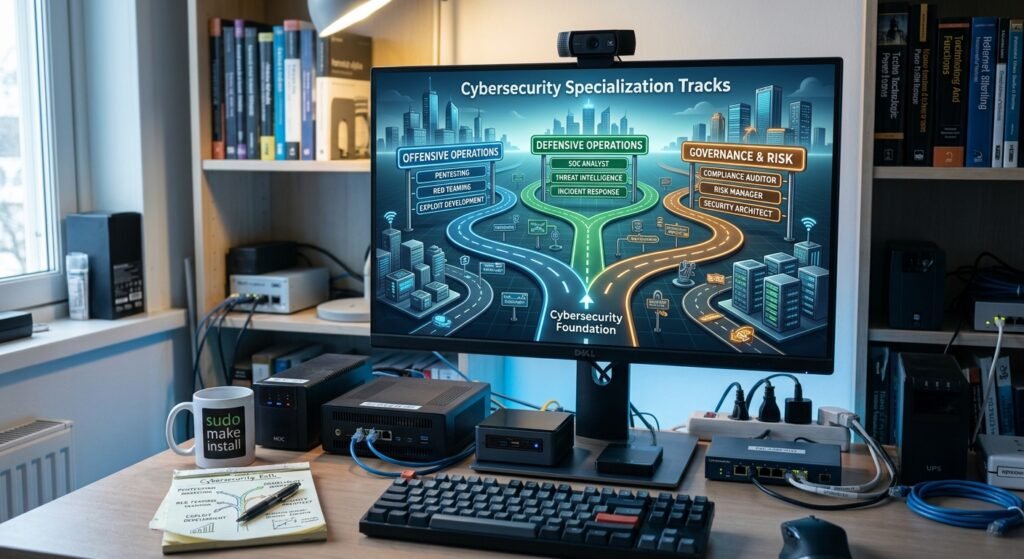
Pick a lane based on what you actually enjoyed at Stage 2 — the analyst who loved digging into an incident belongs in blue team or IR; the one who kept finding creative ways to break the test environment belongs in offensive security.
Stage 4: Mid-Career Depth (5–10 years)
Goal: Go from “competent specialist” to “the person others ask when something’s genuinely hard.”
At this stage, titles shift toward Senior Analyst, Security Engineer, Penetration Tester, Security Architect, or Incident Response Lead, depending on your track. The work changes shape too — less following a runbook, more building the runbook. You start:
- Designing systems and processes, not just operating them
- Mentoring junior team members
- Owning a domain (e.g. “the cloud security posture” or “the detection engineering pipeline”) rather than a queue of tickets
Certifications matter less here than demonstrated impact — a strong OSCP, CISSP, or specialty cloud certification still helps for hiring filters and pay bands, but portfolio, references, and conference talks or write-ups carry increasing weight.
This is also the stage where a lot of people either go deep technical (toward Principal Engineer / Architect) or pivot toward management (Security Team Lead / Manager). Both are valid — the field genuinely needs both tracks, and neither is a “downgrade” from the other.
Stage 5: Senior and Expert Level (10+ years)
Goal: Shape strategy, not just execute it.
At this point, career paths diverge into a few recognizable shapes:
- Principal / Staff Engineer — deep technical authority, often without direct reports, solving the hardest problems in the organization
- Security Architect — designing security into systems and infrastructure at an organizational level
- Director / VP of Security — managing teams, budget, and organizational risk posture
- CISO — accountable for the organization’s entire security program, reporting to executive leadership or the board
- Independent consultant / founder — many senior practitioners eventually go independent, running their own consultancy or training business
Certifications at this level: CISSP is close to a de facto requirement for many leadership-track roles. CCISO or an MBA-adjacent credential becomes relevant if you’re aiming specifically for CISO. For technical tracks, the certifications matter less than a track record of speaking, publishing research, or leading widely recognized projects.
What Stays Constant at Every Stage
A few things matter the entire way through, regardless of where you are on the roadmap:
- Hands-on skill decays if you stop practicing. Even senior architects benefit from staying technically current.
- Communication is a career-long multiplier. The ability to explain risk to a non-technical executive is what separates a senior analyst from a security leader.
- The threat landscape moves. What you learned in Stage 1 will be outdated in a few years — ongoing learning isn’t optional at any level.
The Bottom Line
There’s no single “correct” pace for this roadmap — some people specialize within eighteen months, others take five years finding their track, and both are normal. What matters is that each stage has a clear goal: build fundamentals, get hands-on evidence and land your first role, pick a specialization deliberately rather than by accident, build depth until you’re the go-to person in your domain, then decide whether your next chapter is deep technical mastery or organizational leadership.
Wherever you are on this map right now, the next step is usually smaller than it feels — one certification, one lab, one portfolio post at a time.
Leave a Reply