The Coalition Against Insurance Fraud estimates fraud costs the US insurance industry roughly $308.6 billion a year, spread across healthcare, property and casualty, and workers’ compensation claims. That cost eventually lands on everyone else’s premiums, which is exactly why claims teams have spent the last decade building out a capability that used to belong almost entirely to intelligence agencies and investigative journalists: open-source intelligence.
Here’s how claims and special investigation units actually use OSINT today, what it catches, and where the real limits are.
Why social media became a standard claims tool
For most of the industry’s history, fraud investigation relied on recorded statements, scene canvasses, medical records, and witness interviews. Those tools haven’t gone away, but social media has become a genuinely valuable complement to them, not a replacement. Industry research puts social media evidence as relevant in roughly 30 to 40% of investigated fraud cases overall, and in workers’ compensation specifically, contradictions between social media activity and a claimed injury show up in about one in three investigated claims. That’s a large enough share that most special investigation units now treat a social media review as a routine step, not an exceptional one.
What the investigation actually looks for
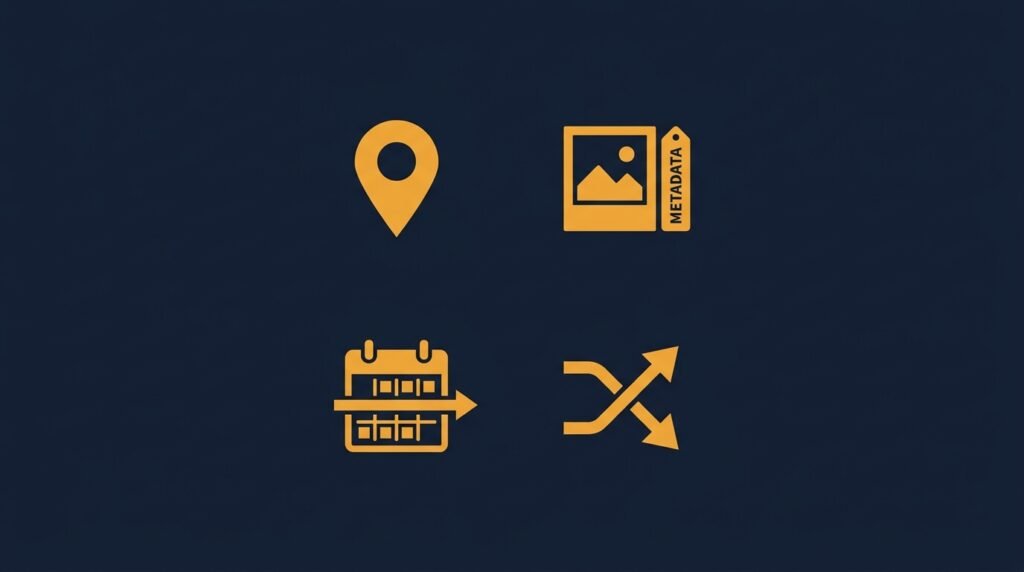
A real OSINT review in a claims context tends to follow a consistent pattern:
- Identify every account tied to the claimant, including aliases and alternate usernames, not just the first profile that turns up in a basic search.
- Review what’s publicly visible, posts, photos, videos, comments, and check-ins, for anything that conflicts with the claim as described.
- Check photo and video metadata, since embedded timestamps and GPS data can confirm or contradict where and when someone claims to have been.
- Look for geo-tagged activity, sometimes called geo-fencing, pulling location-based posts from the area and time window relevant to the claim, which can also surface unknown witnesses who weren’t part of the original statement.
- Cross-reference against public records — property records, business filings, court records — to check details like claimed residency or business operating status that a claim depends on.
A personal injury claim describing an inability to work, paired with recent posts showing physically demanding activity, is the textbook example, and it’s exactly the kind of inconsistency this process is built to surface.
Finding fraud rings, not just single false claims
Some of the more consequential findings aren’t about one person lying on one claim, they’re about a network. A staged-accident participant’s social media connections can reveal links to other claimants filing from the same incident, the same clinic, or the same circle of associates, a pattern investigators only catch by mapping relationships rather than reviewing each claim in isolation. This is the same discipline we covered in our post on link analysis: treating each account or claimant as a node, and the real finding isn’t any single connection, it’s the cluster that forms once enough of them are mapped together.
How AI is accelerating this work
This is one of the fastest-changing parts of claims work right now. AI-assisted platforms built specifically for insurance fraud, including tools like Fivecast MATRIX, use generative AI against customizable screening criteria to flag patterns commonly associated with fraud, automating the slowest part of the old process: manually searching, reading, and cross-referencing every claimant by hand. Some vendors in this space report compressing investigation timelines from two weeks or more down to hours, with coverage extending to a much larger share of flagged claims than a purely manual team could ever review. Those are vendor-reported figures worth treating as directional rather than settled industry-wide numbers, but the underlying shift, from occasional manual review to continuous, largely automated screening, matches what we’ve covered elsewhere in this series about OSINT moving from search to stream.
Why human review still matters here
As covered in our post on the human-in-the-loop problem, automation surfacing more potential leads isn’t the same as automation reaching correct conclusions. A photo showing physical activity doesn’t automatically disprove an injury, timing, context, and medical nuance all matter, and an AI tool flagging a pattern is a lead to investigate, not a finding to act on by itself. The claims teams getting the most reliable results treat AI-OSINT tools the way the rest of this field treats automation generally: a way to cover far more ground, reviewed and interpreted by a trained investigator before anything becomes part of a claims decision.
Staying inside the legal and ethical lines
A few principles separate a defensible investigation from one that creates legal exposure of its own:
- Public information only. Legitimate claims OSINT stays within what’s genuinely publicly accessible, it doesn’t involve attempting to access private accounts, impersonating someone to gain access, or any method that would itself be improper.
- Preserve findings properly. Content gets deleted constantly, so investigators capture and archive what they find in a way that will hold up if it’s later needed as evidence, rather than relying on a screenshot that can’t be authenticated.
- Document the reasoning, not just the conclusion. A finding needs to show how it was reached and from what source, the same discipline covered in our posts on link analysis and the OSINT toolkit.
- Know your jurisdiction’s limits. Rules around what can be collected, how long it can be retained, and how it can be used vary by state and by claim type, and investigators who skip this step risk having otherwise solid findings excluded later.
The bottom line
OSINT has become a standard, not exceptional, part of serious claims investigation, because it works: social media evidence shows up in roughly a third of investigated fraud cases, and network analysis catches coordinated fraud rings that claim-by-claim review would miss entirely. AI is accelerating the collection side dramatically, but the actual decision, whether a pattern genuinely proves a claim is fraudulent, still depends on a trained investigator weighing context an algorithm can’t fully capture on its own.
This builds directly on our earlier posts on link analysis and the human-in-the-loop problem — both worth reading alongside this one if fraud investigation is part of your work.
Leave a Reply